Policies and procedures
Documents with coding, revisions and a multi-level approval workflow. There is one version in force, with who approved it and when.
TISAX
TISAX asks you to show that information security is governed along the automotive supply chain. SGQM keeps the management side in order: documents, audits, actions, training and suppliers.
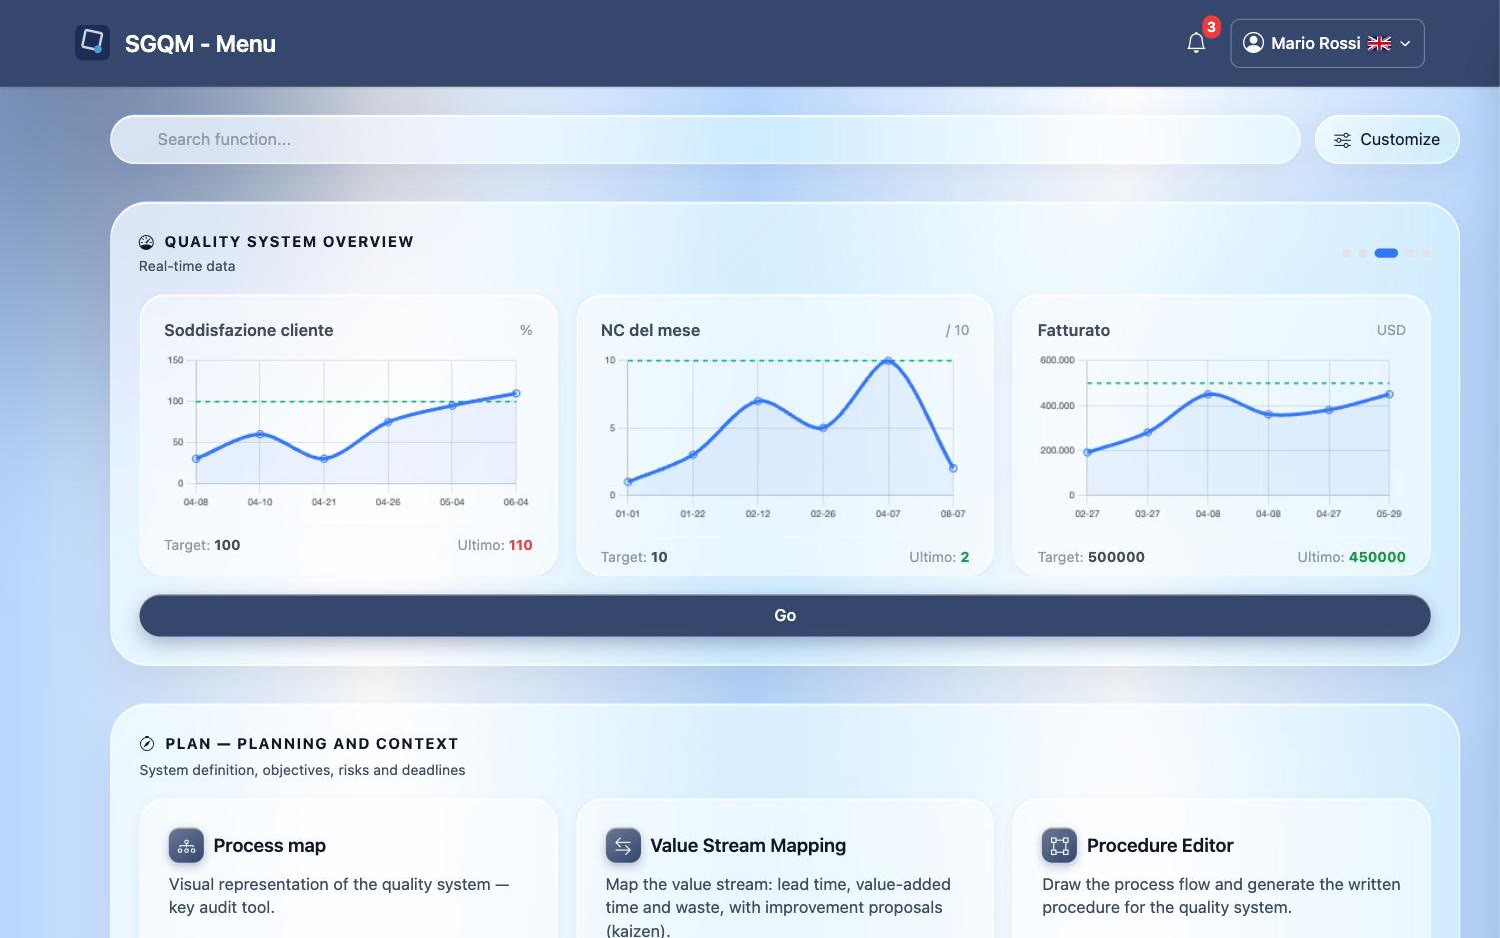
The TISAX assessment is based on the VDA ISA catalogue and checks, beyond technical measures, that policies, responsibilities and controls are defined, applied and reviewed. It is a matter of evidence, which SGQM keeps in order.
Documents with coding, revisions and a multi-level approval workflow. There is one version in force, with who approved it and when.
Audit planning, recording of evidence and findings, link to corrective actions.
Each finding becomes an action with an owner and a due date, chased automatically until closure is verified.
Training plan and course records on information security, with monitored deadlines.
Supplier register and evaluation. For reports that concern them they reply through a protected, expiring link, without accessing your system.
Record of processing activities and data protection impact assessments (DPIA) in the same system, with their deadlines.
No. The assessment is carried out by an accredited audit provider and results are exchanged on the ENX portal. SGQM helps you prepare and maintain the evidence for the management side.
No. It does not replace technical measures. It manages documents, audits, actions, training, suppliers and deadlines.
Yes. Several standards live in the same integrated system.
Contact
Fill in the form and we'll get back to you within 24 hours to arrange a personalised demo.